# \[OBSOLETE, SOLVED\] Email messages not signed with DKIM
**URL:** https://discuss.freedombox.org/t/obsolete-solved-email-messages-not-signed-with-dkim/2387
**Category:** Support
**Created:** [December 15, 2022, 7:10pm UTC](https://discuss.freedombox.org/t/obsolete-solved-email-messages-not-signed-with-dkim/2387 "2022-12-15T19:10:24Z")
**Posts on this page:** 20
**Page:** 1
### Author:  [@Ged](https://discuss.freedombox.org/u/Ged)
#### Post date: [December 15, 2022, 7:10pm UTC](https://discuss.freedombox.org/t/obsolete-solved-email-messages-not-signed-with-dkim/2387/1 "2022-12-15T19:10:25Z")
AS OF FBX 25.1, THIS ISSUE HAS BEEN RESOLVED AND DOES NOT REQUIRE USER INTERVENTION TO GET DKIM SIGNING WORKING.
**Problem Description**
Mail-testers (specifically Port25 Verifer) are responding to my emails with `dkim=none reason="message not signed"`
**Steps to Reproduce**
1. Login to Roundcube
2. Compose message with subject, body and add mail-tester to recipient
3. Send Email
4. Received email report / test result fails dkim because message is not signed.
**Expected Results**
Pass dkim tests
**Additional Info**
Checking DNS records with `dkim` selector respond with a positive key result. No issues with DNS settings - they comply to plinth specified keys.
**Information**
- _FreedomBox version_: FreedomBox version 22.26
- _Hardware_: Raspberry Pi4
- _How did you install FreedomBox?_: Through Debian repos
_Note: Anyone with a brief description on how FBX signs emails would also be appreciated. As far as I understand, FBX doesnt use tools like OpenDKIM so I cant seem to find any online resources to actually know where I can intervene or understand what may cause the problem. Thanks again._
---
### Author:  [@Ged](https://discuss.freedombox.org/u/Ged)
#### Post date: [December 16, 2022, 7:21pm UTC](https://discuss.freedombox.org/t/obsolete-solved-email-messages-not-signed-with-dkim/2387/2 "2022-12-16T19:21:21Z")
Looks like rspamd is resposible for signing DKIM.
in `/etc/postfix/main.cf` noticed
> non\_smtpd\_milters = inet:127.0.0.1:11332
> smtpd\_milters = inet:127.0.0.1:11332
additionally, `/var/lib/rspamd/dkim/` holds a key to the domain…
why then doesn’t rspamd sign the outgoing e-mails?
also noticed that as per [DKIM signing module](https://rspamd.com/doc/modules/dkim_signing.html) there should be a `dkim_signing.conf` file somewhere under `/etc/rspamd/local.d` which doesnt seem to exist…
or am I all in the wrong direction ?.. hmph…
---
### Author:  [@Ged](https://discuss.freedombox.org/u/Ged)
#### Post date: [February 2, 2023, 3:51pm UTC](https://discuss.freedombox.org/t/obsolete-solved-email-messages-not-signed-with-dkim/2387/3 "2023-02-02T15:51:45Z")
Anyone have any thoughts about this… my self - hosted email is now being blocked by google…
---
### Author:  [@timmy](https://discuss.freedombox.org/u/timmy)
#### Post date: [February 2, 2023, 5:59pm UTC](https://discuss.freedombox.org/t/obsolete-solved-email-messages-not-signed-with-dkim/2387/4 "2023-02-02T17:59:43Z")
Is there a sample of the dkim\_signing.conf you could use to create a correct config for yourself?
I’m woefully inexperienced on email setups.
---
### Author:  [@Ged](https://discuss.freedombox.org/u/Ged)
#### Post date: [February 2, 2023, 8:52pm UTC](https://discuss.freedombox.org/t/obsolete-solved-email-messages-not-signed-with-dkim/2387/5 "2023-02-02T20:52:32Z")
There are samples online (i.e. [rspamd dkim signing module web page](https://www.rspamd.com/doc/modules/dkim_signing.html)). Though, Freedombox setup does not align with the file locations stated on this website. So, a. I dont know where I should place a config file for dkim signing b. rspamd configuration is also different from default rspamd setup - I cant even figure out how to check if its configured to sign.
---
### Author:  [@ziomatt](https://discuss.freedombox.org/u/ziomatt)
#### Post date: [February 5, 2023, 1:05am UTC](https://discuss.freedombox.org/t/obsolete-solved-email-messages-not-signed-with-dkim/2387/6 "2023-02-05T01:05:22Z")
Have you found out anything new? I’m pretty sure I’m having the same problem. For me, the mail check reports that the DKIM is not aligned. However, if I look at an email I sent to my gmail account, I’m not seeing the DKIM line like I do on emails I’ve received from other senders.
FreedomBox version: 23.2
Hardware: Pioneer Edition FreedomBox
How did I install FreedomBox? Pioneer Edition Images
I also found the private key in the same location that you did, and I also found an error message in the logs via Cockpit along these lines:
[https://lists.rspamd.com/pipermail/users/2019-July/000831.html](https://lists.rspamd.com/pipermail/users/2019-July/000831.html)
When I looked at the permissions, it was read-only for root. So, I tried changing the ownership to the \_rspamd user, and I updated the permissions to include the write permission. I also rebooted the FreedomBox. I no longer saw the error message in the logs (not even the prior one), but email messages still aren’t being signed.
Oddly, I don’t see the error message coming up after changing the ownership and permissions back, restarting the server, and sending an email.
As for knowing whether it is set up to sign emails, I do see an entry in the log (via Cockpit) about loading a module:
kecb3d\>; cfg; rspamd\_init\_lua\_filters: init lua module dkim\_signing from /usr/share/rspamd/plugins/dkim\_signing.lua; digest: 58702b0f6d
I’m looking at “Debug” level logs. Though, I’m not familiar enough to read the code.
---
### Author:  [@ziomatt](https://discuss.freedombox.org/u/ziomatt)
#### Post date: [February 6, 2023, 3:20pm UTC](https://discuss.freedombox.org/t/obsolete-solved-email-messages-not-signed-with-dkim/2387/7 "2023-02-06T15:20:40Z")
Okay, over the weekend, I was able to find some more information on this. Apparently, a good portion of the capability was added over the summer of '21 as part of the Google Summer of Code. As part of that effort, a checklist was created and it does look like the work stopped short of implementing full DKIM functionality:
> **[Add app for managing a full mail server setup (#56) · Issues · FreedomBox /...](https://salsa.debian.org/freedombox-team/freedombox/-/issues/56)**
>
> Tasks The following is the implementation plan/TODOs for mail server app in FreedomBox:
I did also notice that there are a number of entries in the historical Release Notes. So, more may have been done, but it’s a start. One nice thing is that there are paths to files and at least initial information about enabling it. So, we should be able to check that. Anyway, I probably won’t get back to this until at least this coming weekend, but I thought I’d pass this along.
---
### Author:  [@ziomatt](https://discuss.freedombox.org/u/ziomatt)
#### Post date: [February 18, 2023, 9:08pm UTC](https://discuss.freedombox.org/t/obsolete-solved-email-messages-not-signed-with-dkim/2387/9 "2023-02-18T21:08:20Z")
Yeah, it would be nice if the wiki pages and the manual were more clear about what _is_ implemented and what _will be_ implemented. That said, I love the fact that they have created a project where we can collaborate in standing up what we want. Once I finish getting the main things working for myself, I think the first thing I’ll do is to try to clean up the existing documentation. Then, maybe I’ll be in a position to actually contribute to the functionality.
Anyway, I was finally able to get back to this, and it was about as easy as following the instructions in that issue I referenced above. Here are the notes (verbose for anyone else who happens to come across this).
I started with the example dkim\_signing.conf file on the page you referenced ([DKIM signing module](https://www.rspamd.com/doc/modules/dkim_signing.html)). Saving it to /etc/rspamd/local.d/dkim\_signing.conf. I then made sure these options (referenced in the issue) were set as indicated:
> path = “/var/lib/rspamd/dkim/$domain.$selector.key”;
> selector\_map = “/etc/rspamd/dkim\_selectors.map”;
> allow\_username\_mismatch = true;
> use\_esld = false;
rspamd replaces $domain and $selector with the entries from the map file (covered in the next paragraph). After that, I updated these settings in hopes of seeing log messages if the DNS configuration happened to be wrong:
> check\_pubkey = true;
> allow\_pubkey\_mismatch = false;
Then, I created the file /etc/rspamd/dkim\_selectors.map with the two values. In this case, the “timestamp” is the selector (“dkim”). So, it’s
> {domain} dkim
with {domain} replaced with the actual domain.
Next, I updated the owner and permissions of /var/lib/rspamd/dkim/{domain}.dkim.key:
> chown \_rspamd:\_rspamd /var/lib/rspamd/dkim/{domain}.dkim.key
> chmod u+w /var/lib/rspamd/dkim/{domain}.dkim.key
With that, I restarted rspamd:
> /etc/init.d/rspamd restart
and the next email I sent was signed.
Let me know if you are able to get it to work.
---
### Author:  [@Ged](https://discuss.freedombox.org/u/Ged)
#### Post date: [February 19, 2023, 10:29am UTC](https://discuss.freedombox.org/t/obsolete-solved-email-messages-not-signed-with-dkim/2387/10 "2023-02-19T10:29:55Z")
Worked like a charm, thank you : )
---
### Author:  [@Ged](https://discuss.freedombox.org/u/Ged)
#### Post date: [March 14, 2023, 9:09am UTC](https://discuss.freedombox.org/t/obsolete-solved-email-messages-not-signed-with-dkim/2387/12 "2023-03-14T09:09:37Z")
A side note:
While reading through [this](https://salsa.debian.org/freedombox-team/freedombox/-/issues/56), I discovered that you can easily configure ARC once you have DKIM working.
To do so, (after configuring DKIM) copy configuration for ARC (with sudo as necessary)
```auto
cp /etc/rspamd/local.d/dkim_signing.conf /etc/rspamd/local.d/arc.conf
```
---
### Author:  [@antidoto](https://discuss.freedombox.org/u/antidoto)
#### Post date: [April 1, 2023, 3:10pm UTC](https://discuss.freedombox.org/t/obsolete-solved-email-messages-not-signed-with-dkim/2387/13 "2023-04-01T15:10:10Z")
Although I did all the steps as described by [ziomatt](https://discuss.freedombox.org/u/ziomatt) my mail is still getting marked as spam by gmail.
Also when I send message to another carrier (posteo) I get the response:
* * *
This is the mail system at host [mygreatdomain.net](http://mygreatdomain.net).
I’m sorry to have to inform you that your message could not
be delivered to one or more recipients. It’s attached below.
For further assistance, please send mail to postmaster.
If you do so, please include this problem report. You can
delete your own text from the attached returned message.
The mail system
[anotheruser@posteo.net](mailto:anotheruser@posteo.net): host [mx03.posteo.de](http://mx03.posteo.de)[185.67.36.70] said: 550 5.7.1 Service
unavailable; client [_hidden by me]_ blocked using [zen.spamhaus.org](http://zen.spamhaus.org) (in
reply to RCPT TO command)
* * *
Is there a way to troubleshoot?
Is it possible that the reason is that my ISP doesn’t provide me with a static ip ?
I got two test results in [mail-tester.com](http://mail-tester.com), one was 7.9 and the other was 5.9
Lastly when I create /etc/rspamd/local.d/arc.conf I get a message connection failed from two e-mail clients.
---
### Author:  [@antidoto](https://discuss.freedombox.org/u/antidoto)
#### Post date: [April 2, 2023, 12:52pm UTC](https://discuss.freedombox.org/t/obsolete-solved-email-messages-not-signed-with-dkim/2387/14 "2023-04-02T12:52:52Z")
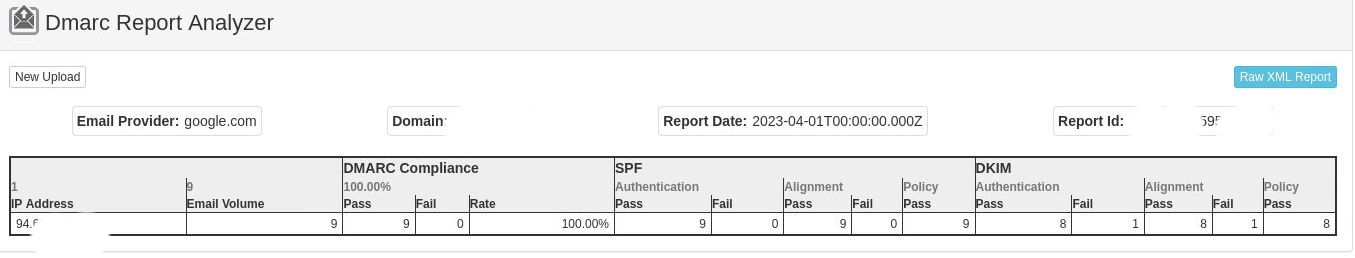
This is the Dmarc Report from google
---
### Author:  [@Ged](https://discuss.freedombox.org/u/Ged)
#### Post date: [April 3, 2023, 7:01am UTC](https://discuss.freedombox.org/t/obsolete-solved-email-messages-not-signed-with-dkim/2387/15 "2023-04-03T07:01:11Z")
Both 5.9 and 7.9 on mail-tester are low even without DKIM signature.
You may have misconfigured your signature file but it may also be that your server is somewhat compromised [(which happened to me)](https://discuss.freedombox.org/t/solved-dovecot-root-user-error-log-flood/2474/4).
I suggest revert back to the initial installation configuration and check your mail queue and logs with ;
a. run `mailq` in terminal. Check if you have outgoing mails that you didnt actually send.
b. check your logs with `journalctl -u postfix@-.service` to see if there is any mail you didnt actually send.
If you think there are any problems, I suggest take it from there.
Hope it helps.
---
### Author:  [@antidoto](https://discuss.freedombox.org/u/antidoto)
#### Post date: [April 3, 2023, 10:08am UTC](https://discuss.freedombox.org/t/obsolete-solved-email-messages-not-signed-with-dkim/2387/16 "2023-04-03T10:08:18Z")
Thank you for your suggestions,
I did run the commands you proposed and:
a. empty
b. Didn’t showed something suspicius, although I do not know exactly what I should look
About mail-tester. the main problem is:
→ |-1.274|RDNS\_NONE|Delivered to internal network by a host with no rDNS
**This may indicate you do not have a rDNS configured for your hostname or the rDNS does not match your sending IP** |
### Your reverse DNS does not match with your sending domain.
Your IP address \*_MY ACTUAL PUBLIC IP_ is associated with the domain **3(NXDOMAIN)**.
Nevertheless your message appears to be sent from **my [domain.net](http://domain.net)**.
You may want to publish a pointer (PTR type) DNS record with a value of **[mydomain.net](http://mydomain.net)** or use **3(NXDOMAIN)** as hostname in your mail software
Here are the tested values for this check:
- IP: (MY ACTUAL PUBLIC IP)
- HELO: [mydomain.net](http://mydomain.net)
- rDNS: 3(NXDOMAIN)
So my question is:
Is it possible to set rdns without an external static ip?
---
### Author:  [@Ged](https://discuss.freedombox.org/u/Ged)
#### Post date: [April 3, 2023, 12:11pm UTC](https://discuss.freedombox.org/t/obsolete-solved-email-messages-not-signed-with-dkim/2387/17 "2023-04-03T12:11:12Z")
Hi,
Sorry, I believe thats something you can only solve with your ISP.
Here in my country, I practically sent an email to my ISP for rDNS (PTR) and they changed it. I was not something in my control.
---
### Author:  [@antidoto](https://discuss.freedombox.org/u/antidoto)
#### Post date: [April 3, 2023, 4:32pm UTC](https://discuss.freedombox.org/t/obsolete-solved-email-messages-not-signed-with-dkim/2387/18 "2023-04-03T16:32:05Z")
I am now a little bit lost.
I will continue to expand my noobness though in the pursuit to understand. Maybe it will help others in the future…
What am I expecting from my ISP? an ipv4 address? a domain name?
Will I need to update my DNS records with the value/address/domain that my ISP will provide me in order to enable reverse dns to my domain? Is there an example I can follow?
Thank you all for your patience.
---
### Author:  [@Avron](https://discuss.freedombox.org/u/Avron)
#### Post date: [April 3, 2023, 7:36pm UTC](https://discuss.freedombox.org/t/obsolete-solved-email-messages-not-signed-with-dkim/2387/19 "2023-04-03T19:36:20Z")
> [@antidoto](#):
>
> What am I expecting from my ISP? an ipv4 address? a domain name?
If your IPv4 address is a.b.c.d, you need a DNS record such as:
d.c.b.a.in-addr.arpa PTR [mydomain.net](http://mydomain.net)
It points an IP address to a name (instead of the opposite in the usual usage of DNS). Only the entity that owns the address a.b.c.d can do that, so probably your ISP. Some ISPs accept doing that, others don’t (one ISP in my country provides an interface to do that, my current ISP simply does not allow that at all).
---
### Author:  [@antidoto](https://discuss.freedombox.org/u/antidoto)
#### Post date: [November 13, 2023, 4:02am UTC](https://discuss.freedombox.org/t/obsolete-solved-email-messages-not-signed-with-dkim/2387/20 "2023-11-13T04:02:52Z")
After many tests using dynamic IP (all failed), moving to a static IP solved the issue for me.
Thank you all!
---
### Author:  [@jag](https://discuss.freedombox.org/u/jag)
#### Post date: [January 2, 2024, 4:08am UTC](https://discuss.freedombox.org/t/obsolete-solved-email-messages-not-signed-with-dkim/2387/21 "2024-01-02T04:08:12Z")
Hello from 2024! Thank you so much for creating this post my emails are now properly signed. Does this get config get backed up by FreedomBox automatically in case I needed to restore?
---
### Author:  [@Ged](https://discuss.freedombox.org/u/Ged)
#### Post date: [January 2, 2024, 4:21am UTC](https://discuss.freedombox.org/t/obsolete-solved-email-messages-not-signed-with-dkim/2387/22 "2024-01-02T04:21:16Z")
Hi @jag
Happy new year. Yes, FBX backs up your config so you dont have to reconfigure these settings if you restore from your backup.
Cheers.
[Next page](https://discuss.freedombox.org/t/obsolete-solved-email-messages-not-signed-with-dkim/2387.md?page=2)