# Fail2ban enable apache-noscript
**URL:** https://discuss.freedombox.org/t/fail2ban-enable-apache-noscript/4378
**Category:** Tips and Tricks
**Created:** [September 21, 2026, 12:44am UTC](https://discuss.freedombox.org/t/fail2ban-enable-apache-noscript/4378 "2026-09-21T00:44:04Z")
**Posts on this page:** 3
**Page:** 1
### Author:  [@joseph](https://discuss.freedombox.org/u/joseph)
#### Post date: [September 21, 2026, 12:44am UTC](https://discuss.freedombox.org/t/fail2ban-enable-apache-noscript/4378/1 "2026-09-21T00:44:04Z")
I have a heap of log entries like this today:

Some AI tells me that this is caused by a client trying to execute a PHP script I don’t have or to which they do not have permission. It appears there’s an app for that: fail2ban apache-noscript
The outcome I’d like is for these clients to get banned, so I’m going to try out a new fail2ban jail which I’ve never done before. I’m going to lean on the freedombox configurations and see if I can’t get this right.
Look in /etc/fail2ban/jail.d and you’ll see apache-auth-freedombox.conf. I’m using this as a template.
`$ cat apache-auth-freedombox.conf
[apache-auth]
enabled = true
# Tweak the filter regex to work with journal format. Use apache-error as the
# syslog facility
filter = apache-auth[logtype=“journal”,logging=“syslog”,_daemon=“apache-error”]
journalmatch = SYSLOG_IDENTIFIER=apache-error
`
You see that this one has…
> \_daemon=“apache-error”
in the filter line - and if you look at the screen capture that is also an apache-error log entry. It looks like all we do is enable the new jail with the same configuration elements.
I’m trying this as a new file named ~~/etc/fail2ban/apache-noscript-local.conf~~ /etc/fail2ban/apache-noscript.local (this naming convention is described in the manpage). If it works and I like it, I’ll suggest that we add that to FreedomBox. Here’s what will go in that file:
`[apache-noscript]
enabled = true
# Tweak the filter regex to work with journal format. Use apache-error as the
# syslog facility
filter = apache-noscript[logtype=“journal”,logging=“syslog”,_daemon=“apache-error”]
journalmatch = SYSLOG_IDENTIFIER=apache-error
maxretry = 1
`
And that started without errors.
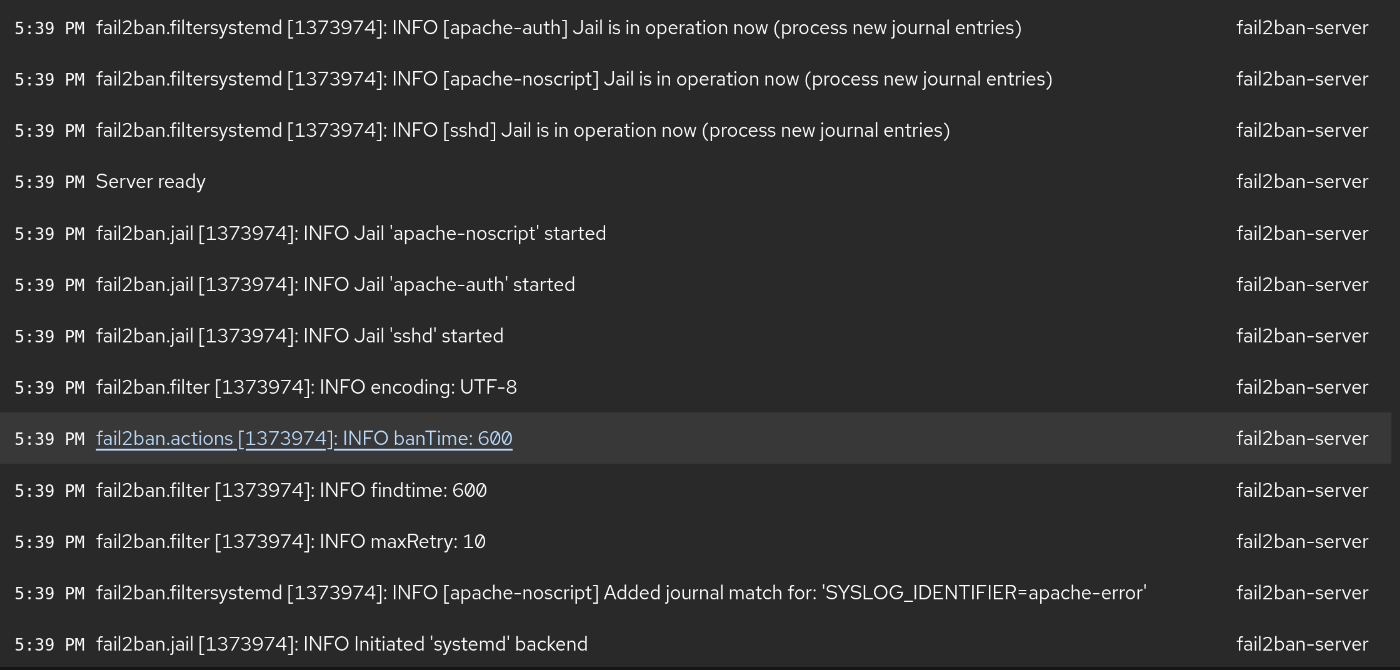
I’ll share a screen shot of some bans when they come in.
---
### Author:  [@joseph](https://discuss.freedombox.org/u/joseph)
#### Post date: [September 21, 2026, 2:51am UTC](https://discuss.freedombox.org/t/fail2ban-enable-apache-noscript/4378/2 "2026-09-21T02:51:25Z")
# Update
In the latest batch of malicious log garbage there was only one ‘Primary script unknown,’ so it did not trigger a ban (I didn’t have maxretry set as 1). But, I did see this!
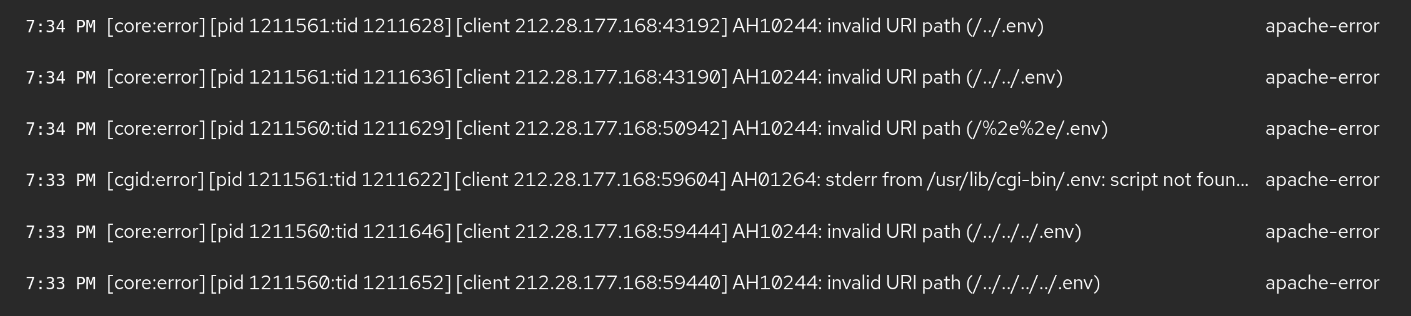
Same thing, different jail. I just enabled the apache-overflows jail. This one was also trivially easy and did not give any errors when I restarted fail2ban. This one is /etc/fail2ban/jail.d/apache-overflows.local.
`[apache-overflows]
enabled = true
# Tweak the filter regex to work with journal format. Use apache-error as the
# syslog facility
filter = apache-overflows[logtype=“journal”,logging=“syslog”,_daemon=“apache-error”]
journalmatch = SYSLOG_IDENTIFIER=apache-error
maxretry = 1
`
I hope to show some results soon!
---
### Author:  [@joseph](https://discuss.freedombox.org/u/joseph)
#### Post date: [September 21, 2026, 4:25am UTC](https://discuss.freedombox.org/t/fail2ban-enable-apache-noscript/4378/3 "2026-09-21T04:25:11Z")
# Banned.

Note the maxretry = 1 for noscript and overflows. Those cover actions that you as a user would not do by mistake - and the ban is applied immediately. This one was banned after the first attempt. Once I’m comfortable with this I’ll increase the bantime from 600 seconds to hours or a day.
You can easily test noscript with [https://freedombox/this-script-does-not-exist.php](https://freedombox/this-script-does-not-exist.php). You’ll ban yourself if you have maxretry = 1, but then you’ll know it’s working as you expect. Unban yourself with `sudo fail2ban-client set apache-noscript unbanip `
apache-noscript seems to be the one. I reduced maxretry from 10 to 3 for sshd, and maxretry = 1 for apache-noscript. After running overnight I have more bans per period and multiple apache-noscript bans.
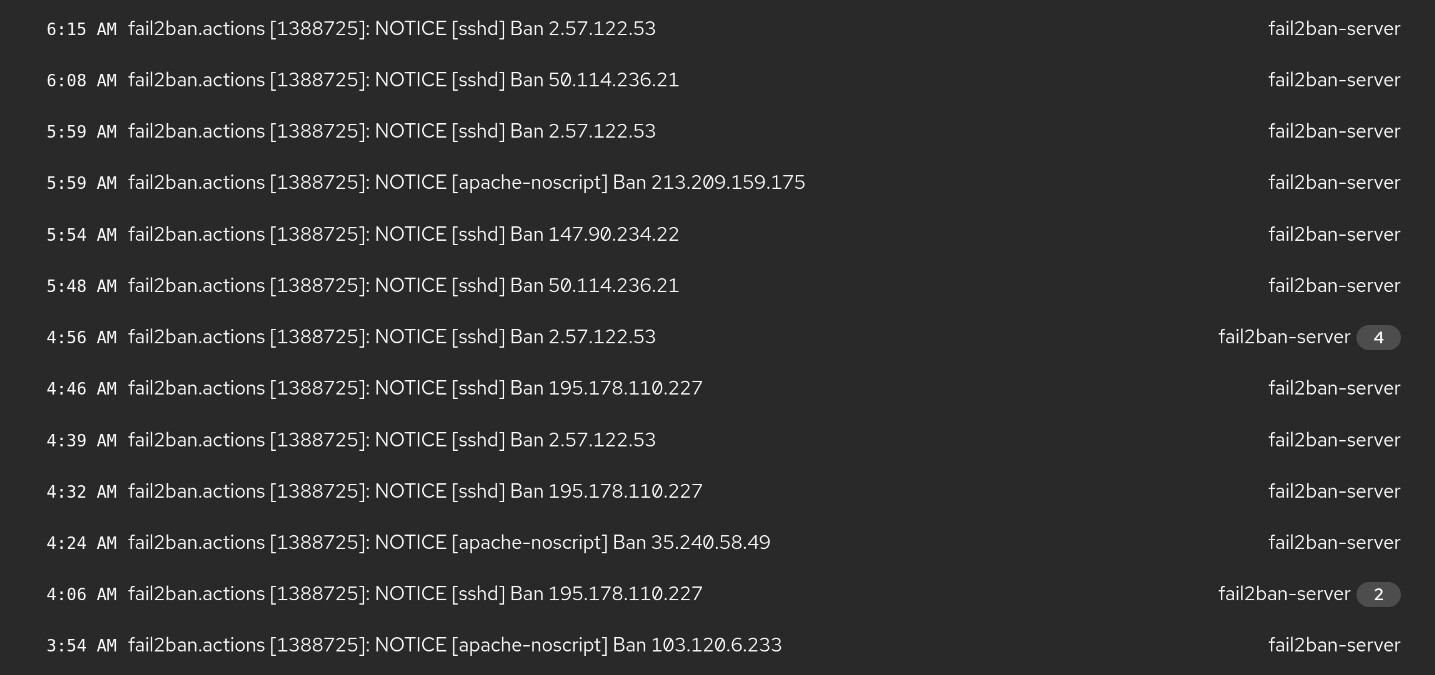
What, if anything did this accomplish?
Probably less than one would hope, but there are
- reduced log entries about this stuff
- better log entries when they get banned 🙂