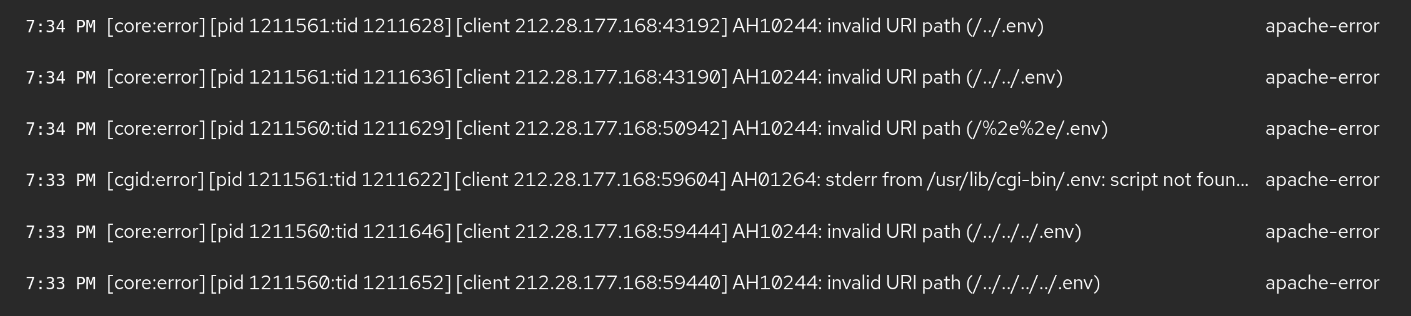
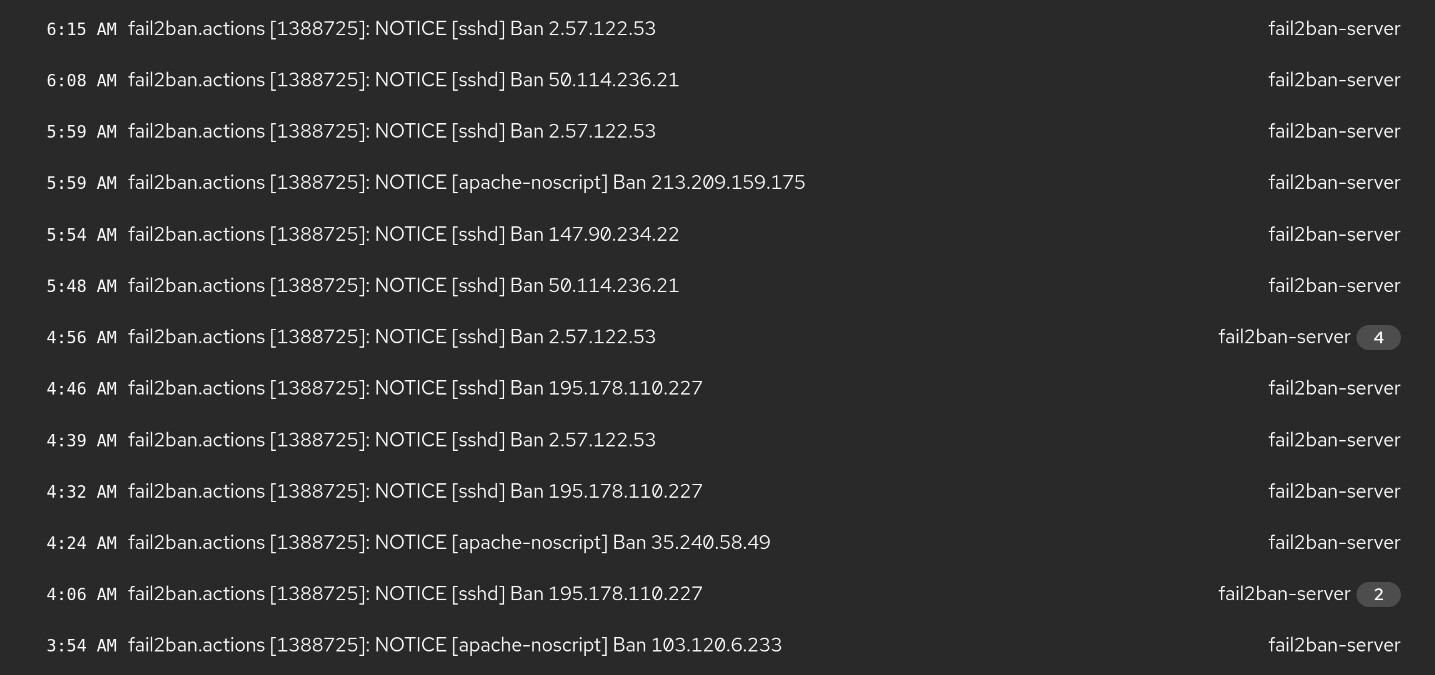
I have a heap of log entries like this today:

Some AI tells me that this is caused by a client trying to execute a PHP script I don’t have or to which they do not have permission. It appears there’s an app for that: fail2ban apache-noscript
The outcome I’d like is for these clients to get banned, so I’m going to try out a new fail2ban jail which I’ve never done before. I’m going to lean on the freedombox configurations and see if I can’t get this right.
Look in /etc/fail2ban/jail.d and you’ll see apache-auth-freedombox.conf. I’m using this as a template.
$ cat apache-auth-freedombox.conf

[apache-auth]

enabled = true

# Tweak the filter regex to work with journal format. Use apache-error as the

# syslog facility

filter = apache-auth[logtype=“journal”,logging=“syslog”,_daemon=“apache-error”]

journalmatch = SYSLOG_IDENTIFIER=apache-error
You see that this one has…
_daemon=“apache-error”
in the filter line - and if you look at the screen capture that is also an apache-error log entry. It looks like all we do is enable the new jail with the same configuration elements.
I’m trying this as a new file named /etc/fail2ban/apache-noscript-local.conf /etc/fail2ban/apache-noscript.local (this naming convention is described in the manpage). If it works and I like it, I’ll suggest that we add that to FreedomBox. Here’s what will go in that file:
[apache-noscript]

enabled = true

# Tweak the filter regex to work with journal format. Use apache-error as the

# syslog facility

filter = apache-noscript[logtype=“journal”,logging=“syslog”,_daemon=“apache-error”]

journalmatch = SYSLOG_IDENTIFIER=apache-error

maxretry = 1
And that started without errors.
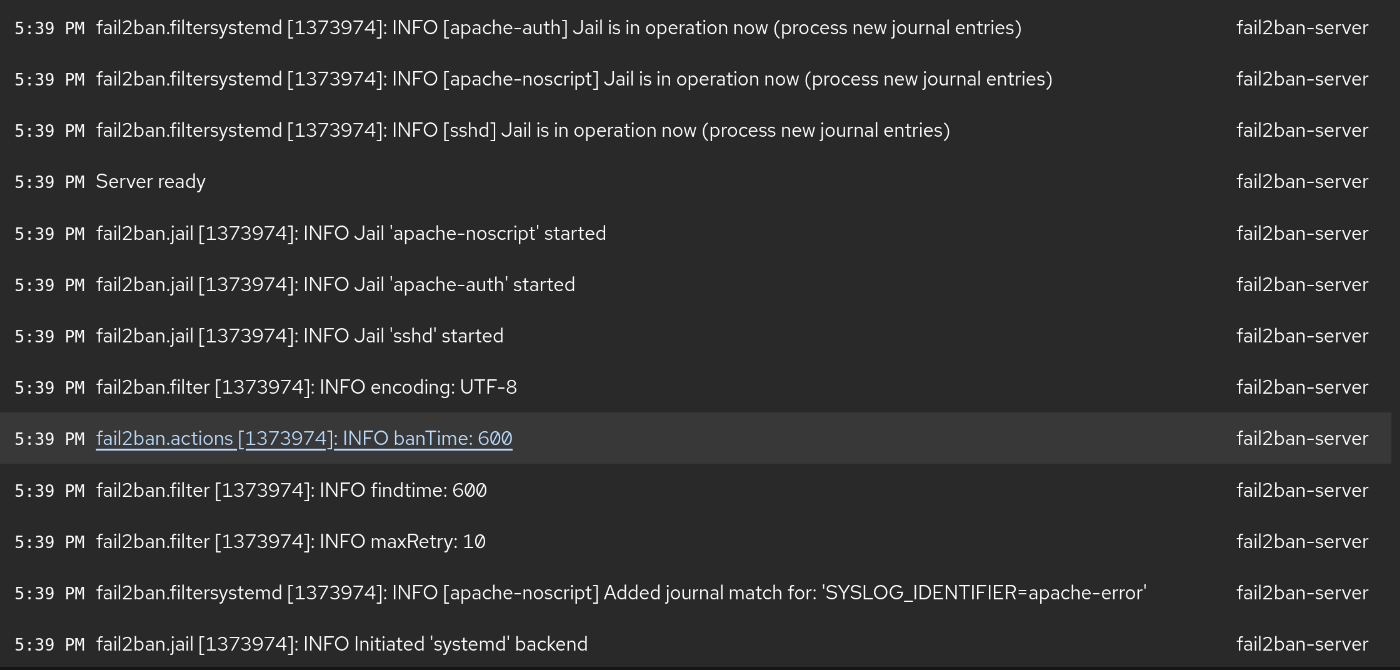
I’ll share a screen shot of some bans when they come in.